About
Hi, I'm Moshe, and I go by ChiefGyk3D online.
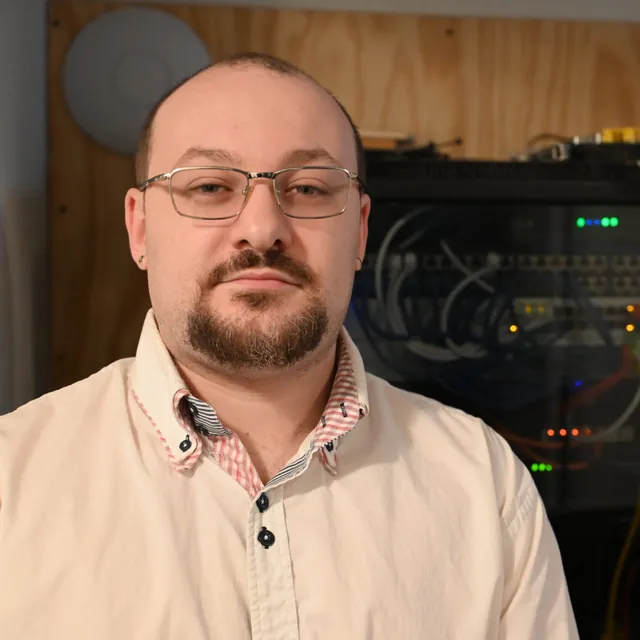
I’m a Senior Cybersecurity Engineer (CISSP), Linux nerd, ham radio operator, open-source builder, and content creator. I’m primarily self-taught. Most of what I know came from curiosity, building things in my homelab, and figuring out why they didn’t work.
My work spans identity and access management, endpoint security, security automation, zero trust, and cloud and network security. I also work with threat modeling, OSINT, telecom security, and SIEM/SOC tooling. That includes IAM, EDR, SOAR, ZTNA, and SASE, along with tools like pfSense, Suricata, Wazuh, and OpenSearch. I’m more than ready for a security architecture role, and that’s where I’m headed.
I run Linux on my desktops and servers, and my homelab is where a lot of my interests come together. It’s a production-style environment built partly from repurposed hardware, with a dual-GPU local AI box and self-hosted services including Mastodon, Matrix, and Pixelfed. Radio is part of that curiosity too, from software-defined radio to Meshtastic and LoRa. I care about end-to-end encryption, zero trust, owning my infrastructure, right to repair, and privacy rights.
In 2026, I spoke at BSides Dayton and COISSA. I also volunteer with the Call Center Village (opens in a new tab).
I share cybersecurity knowledge with more than 500K followers across platforms because I want more people to have access to it. Knowledge is power. Money is power. When you put knowledge behind a price tag, you help keep that power with the people who already have money. I have an ethical issue with that, so I open source a lot of my work and share what I learn.
PHP2Shell made me take another look at how I build for the web, and I wanted a site that was fast, light, and more secure, with a minimal attack surface. So I built it as a static site on Cloudflare Pages, with strict security headers and a small set of pinned scripts. The same drive shows up in my homelab and public repos, where I build and document the systems I want to understand. If I put this much work into my own homelab, you can probably guess what I bring when I work with you.
I am a content creator with over 500,000 followers across platforms, a Kick partner and a Twitch partner, and I work directly with TikTok in their educators program. I make tutorials, security breakdowns, and livestreams about Linux as a daily driver and production environment, cybersecurity investigations, and real-world threat and news breakdowns. I also cover radio and Meshtastic communications, mesh networking, endpoint security, enterprise tooling, home labs, and networking architecture. My content also includes device reviews, privacy tools, and open-source infrastructure.
You’re not dead until you stop learning. Happy hacking.
My resume lists my skills, open-source projects, certifications, and education.
Current projects
- Clouds Against Humanity (GitHub, opens in a new tab)
- Stream Daemon (GitHub, opens in a new tab)
- SIEM Docker Stack (GitHub, opens in a new tab)
- git-your-ship-together (GitHub, opens in a new tab)
- Reach Around (GitHub, opens in a new tab)
- Hammunition (GitHub, opens in a new tab)
- More projects on GitHub (opens in a new tab)
Skills
Identity and access
I work with single sign-on, MFA, passwordless authentication, passkeys, hardware security keys, identity-driven access controls, LDAP integration, and service authentication. Okta, Microsoft Entra, JumpCloud, YubiKey, Delinea.
Endpoint, email, and data security
I work across endpoint detection and response, email security, phishing response, data access visibility, and security platform automation. CrowdStrike, Proofpoint TRAP, Avanan, Varonis.
Network security and zero trust
I handle firewall administration, network segmentation, VLAN design and isolation, intrusion detection and prevention, DNS filtering, remote access architecture, network telemetry, and troubleshooting. Zscaler ZIA and ZPA, Twingate, pfSense CE and pfSense Plus, Suricata, pfBlockerNG, UniFi, MikroTik.
Security operations and investigation
My work includes log collection, forwarding, and analysis, security telemetry, detection, vulnerability management, honeypots and deception, and attack surface analysis. Splunk, Wazuh, OpenSearch, Datadog, Tenable, Wiz, VirusTotal, urlscan, OWASP Threat Dragon.
Cloud, infrastructure as code, and secrets
I build automated infrastructure, manage secrets, design zero-trust access for cloud environments, and create reproducible security labs and educational infrastructure. AWS, DigitalOcean, Terraform, OpenTofu, Spacelift, Doppler, GitHub, Cloudflare.
Linux and homelab
In my homelab, I administer Pop!_OS, Ubuntu, Debian, and Parrot OS systems, run virtualized infrastructure with Proxmox, repurpose hardware for services, and perform serial-console installations. I self-host Mastodon, Matrix, and Pixelfed, including Matrix-Discord bridging.
Software and automation
I develop Python tools and open-source libraries, build API integrations and event-driven bots, connect notification and messaging systems, and use GitHub-based development and code review. My CI work includes security checks, dependency scanning, and linting. GitHub, GitHub Copilot, Snyk, Discord and Matrix integrations, streaming and social-platform integrations.
Local AI and agents
I run local models through Ollama on a dual-GPU server and route work between local and hosted models based on cost and capability. I coordinate agents for drafting, implementation, and review, require human approval for paid model use, and use AI-assisted review alongside conventional CI and security checks.
Radio, RF, and telecom
I work with SDR, Meshtastic, LoRa, APRS and packet radio, RF experimentation, cellular modem integration, and telecom security. HackRF, Meshtastic devices, LoRa radios, and Linux-based radio and SDR tooling.
Where I'm headed
I am a Senior Cybersecurity Engineer with a CISSP, primarily self-taught through homelabbing and hands-on work. I am moving toward a security architecture role.
At a glance
- Desktop
- Pop!_OS, Parrot OS, and Debian on hand-built desktops and laptops from Tuxedo Computers, System76, and MNT. Ubuntu on production servers.
- Radio
- Licensed amateur radio operator. SDR, Meshtastic, LoRa, antenna builds, and a growing toolchain for turning a Linux box into an RF workstation.
- Self-hosted
- My own Mastodon instance, Matrix homeserver, Pixelfed, link aggregator, support page, and more.
- Cares about
- End-to-end encryption, zero trust, owning your infrastructure, right to repair, privacy rights, threat modeling, OSINT, and telecom security.
Hardware and homelab
A production-grade home lab for building, breaking, and learning. I use single-board computers and repurposed hardware wherever practical.
- Network and security
- A Supermicro E300-8D firewall running pfSense, Suricata IDS/IPS, and pfBlockerNG on VLAN-segmented networks. UniFi managed switches and access points send telemetry into Grafana and InfluxDB through UniFi Poller, and device logs go to Wazuh for EDR alerting.
- SIEM server
- A Supermicro SuperServer 5019A-FTN4 with an Intel Atom C3758 and 64 GB of DDR4 ECC, on tiered SSD and NVMe storage. It runs a Dockerized OpenSearch hot/warm cluster with Wazuh, Grafana, Logstash, Prometheus, InfluxDB, Syslog-ng, UniFi Poller, and Portainer.
- AI inference
- The FrankenLLM server runs two GPUs, an NVIDIA RTX 5060 Ti 16 GB and an NVIDIA RTX 3050 8 GB, for simultaneous multi-model inference.
- Compute and storage
- Raspberry Pi 4 and 5, Pine64, and other single-board computers for power-efficient computing. Second-hand PCs repurposed whenever possible to reduce e-waste. A Synology NAS with NUT (Network UPS Tools) monitoring and notifications.
- Radio, SDR, and time
- Meshtastic nodes, LoRa experiments, and custom antenna builds. SDR for ADS-B aircraft tracking, UAT weather, and RF signal analysis. Hammunition builds the workstation, and Hammunition Hill watches propagation from it. In progress: two GPS-disciplined stratum-1 NTP appliances built from Mother Ticker.
- Cloud extension
- Clouds Against Humanity: DigitalOcean droplets managed with OpenTofu through Spacelift, secrets in Doppler, and reachable only over Twingate zero-trust access with zero public inbound ports.
Contact
Email, Discord, and Matrix are on the contact page.